
Automatically collect audit evidence locally.
Stop pulling screenshots before every audit. Automatically collect AWS and GitHub evidence on your own infrastructure. Review its source, freshness and control links, then export a packet for SOC 2, HIPAA or ISO 27001 readiness review.
SOC 2 evidence software from $99/mo per organization.
Published pricing in USD. Unlimited team members. No per-seat fees.
Software subscription. Your infrastructure and audit fees are separate.
Assisted package delivery. You need a suitable Docker host and read-only source access. See a sample evidence packet.
- Local-first deployment
- SOC 2, HIPAA, and ISO 27001 workflows
- GitHub, AWS, Jira, Linear, Google Workspace, Okta, Datadog, and WorkOS; more sources in Preview
- Share verifiable audit packets
- API evidence first, screenshots when needed
Built for engineering-led teams preparing for SOC 2, HIPAA, and enterprise security reviews.
The problem
When an evidence request arrives, can your team produce the right record?
Collecting records, confirming scope and preparing a reviewer packet takes engineering time. Start with one recurring evidence task and check whether AuditFetch reduces that work.
Screenshot scavenger hunts
Engineers waste hours capturing admin panels, access lists, branch settings, and security configurations.
Evidence gets stale
Point-in-time exports expire quickly. By audit time, yesterday’s evidence may no longer satisfy the control period.
Proof lives across systems
A single control may require GitHub, Jira, AWS, Okta, and Google Workspace evidence to tell the full story.
Audit week becomes chaos
The same senior engineers who should be shipping product end up chasing screenshots and CSVs.
The solution
AuditFetch continuously collects, validates, and packages audit evidence for you.
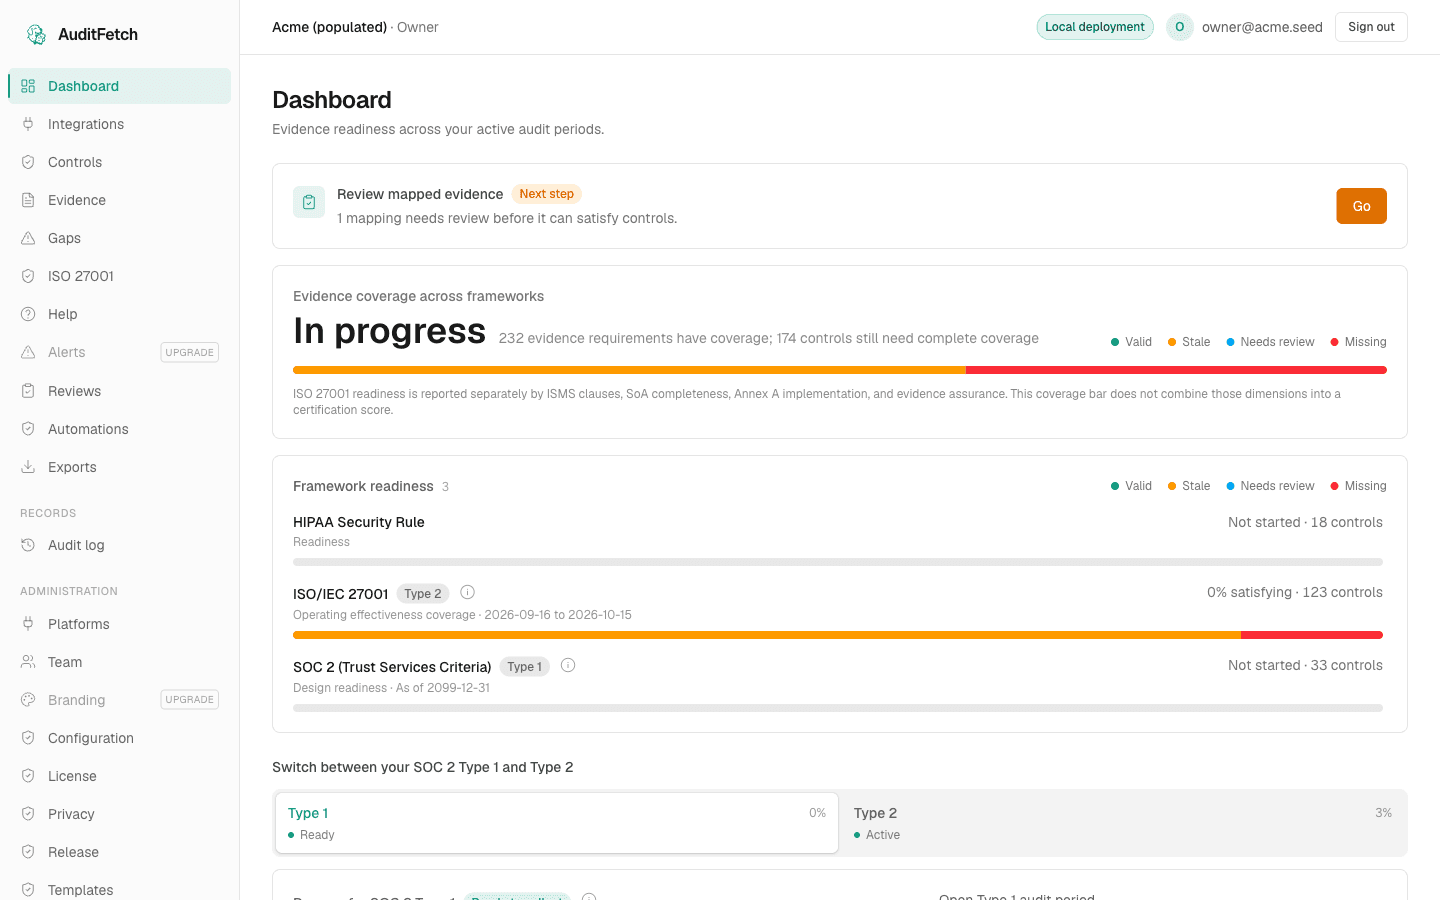
AuditFetch runs evidence collection jobs against your systems, normalizes the results, checks freshness, flags gaps, and creates auditor-ready packets mapped to SOC 2, HIPAA, and ISO 27001 controls.
Continuous evidence collection
Schedule recurring evidence snapshots for access control, change management, logging, monitoring, and security review workflows.
Control-aware evidence mapping
Map evidence artifacts to SOC 2, HIPAA, and ISO 27001 requirements so reviewers know exactly what each artifact supports.
Freshness and gap detection
Detect missing, stale, incomplete, or unmapped evidence before the auditor does.
Auditor-ready packets
Generate PDF, ZIP, CSV, and JSON evidence packages with source metadata, timestamps, hashes, and control links.
Local-first by design
Your evidence should not have to live in another vendor’s cloud.
AuditFetch Local runs inside your environment. Evidence and integration credentials stay under your control by default, and you choose whether to export or sync evidence to other systems. Licensing and update services support local installations without hosting their raw evidence. Managed cloud deployments are a separate offering with selective onboarding.
AuditFetch Local
- Runs in your environment
- Evidence stays local
- Local credentials
- Internal systems supported
- Best for security-sensitive teams
AuditFetch Cloud — managed deployment
Selective onboarding. Managed deployments are separate from the licensing and update services used by local installations. Confirm the available capabilities and data-hosting arrangements with us before purchase.
- Managed hosting by arrangement
- Faster setup
- Managed scheduling
- Team collaboration
We'll confirm availability and scope before anything is purchased.
- Customer-controlled evidence storage
- Customer-controlled integration credentials
- Local Playwright screenshot worker
- Local audit logs
- Optional telemetry, off by default
- No raw evidence sent to AuditFetch Cloud by default
From scattered systems to audit-ready evidence in four steps.
Connect your systems
Connect read-only integrations for GitHub, AWS, Jira, Linear, Google Workspace, Okta, Datadog, and WorkOS. Additional sources are in Preview; check the capability matrix before setup.
Collect evidence automatically
AuditFetch pulls API exports, captures approved screenshots, and stores source metadata with timestamps and hashes.
Map evidence to controls
Evidence is organized against SOC 2, HIPAA, and ISO 27001 control requirements with freshness status, reviewer state, and gap explanations.
Export or sync
Generate packets in PDF, ZIP, CSV, and JSON. Deliver to Vanta (Preview) and Drata (Preview) once configured.
Evidence sources
Collect proof from the systems auditors already ask about.
Engineering
- GitHub
- Jira
- Linear
Cloud & Infrastructure
- AWS
- Datadog
Identity & Access
- Google Workspace
- Okta
- WorkOS
Browser capture
- Browser playbooksPreview
Evaluator only
- Disposable sample workspaceSample data
Compliance Destinations
- ZIP
- CSV
- JSON
- VantaPreview
- DrataPreview
Some integrations are rolling out first. AuditFetch prefers API-based evidence collection and uses controlled browser screenshots only when API evidence is insufficient.
Custom Evidence Automation
Automate the last mile without turning compliance into custom integration work.
Built-in collectors cover common workflows. Custom Evidence Automation securely adapts reviewed read-only operations for AWS and GitHub—then sends the result through the same governed evidence lifecycle as built-in collection.
Find the last-mile gap
See which missing or manual requirement can be supported by a governed collector.
Choose a reviewed template
Start from an approved read-only operation for a supported provider—not a blank API request.
Set your scope
Set the supported resource scope for the reviewed AWS and GitHub template before testing.
Preview and test
Verify access and inspect a bounded, sanitized result before anything is enabled.
Enable deliberately
Promote the tested version only when the source, permissions, and scope are understood.
Reuse governed evidence
The artifact keeps its source, timestamp, mapping, and audit history across compatible controls and frameworks.
Designed for safe, reviewable collection
Automations use existing integration credentials and read-only scopes. With AuditFetch Local, secrets stay in your environment; hosted deployments use their configured secret store. Tests are audited, and evidence remains subject to the same provenance, review, retention, and export controls as built-in collection.
Read the practical automation guideBuilt for SOC 2, HIPAA, and ISO 27001 evidence workflows from day one.
AuditFetch is not a legal opinion engine and does not declare your organization compliant. It helps you prove that the controls you claim to operate have fresh, organized, traceable evidence.
Logical Access
Users, admins, MFA, groups, privileged roles, and access review evidence.
Change Management
PR approvals, branch protection, linked Jira/Linear tickets, and deployment records.
Monitoring
CloudTrail, Security Hub, CloudWatch, Datadog monitors, alert review records.
Incident Response
Incident tickets, postmortems, response timelines, and remediation evidence.
Access Control
Workforce access lists, privileged users, app assignments, and MFA status.
Audit Controls
CloudTrail, application logs, security monitoring, and log retention evidence.
Authentication
MFA enrollment, SSO policies, Okta factors, and Google Workspace Directory enrollment snapshots.
Transmission Security
TLS configuration, encrypted endpoints, load balancer settings, and infrastructure encryption.
AuditFetch helps collect and organize evidence. It does not provide legal advice, guarantee audit acceptance, or certify SOC 2 or HIPAA compliance.
Works with your existing compliance stack
Keep Vanta or Drata. Let AuditFetch do the evidence work.
AuditFetch is designed to complement your compliance platform, not replace it. Collect evidence locally, review it, then export it into the system your team or auditor already uses.
Drata Evidence Library sync
Push AuditFetch-generated evidence into Drata Evidence Library and link it to the relevant controls.
Vanta document upload workflow
Upload AuditFetch evidence into Vanta document requests or evidence targets mapped to your controls.
Auditor-ready export packets
Generate ZIP, PDF, CSV, and JSON packets when your auditor wants evidence outside a platform.
Built for the people who actually get pulled into audit evidence work.
For CTOs and VPs of Engineering
Keep senior engineers focused on product instead of audit screenshots. AuditFetch turns evidence collection into a repeatable workflow.
For Engineering Managers
Know what evidence is missing, stale, or ready before audit week. Review exceptions instead of chasing screenshots.
For fractional CISOs
Run repeatable evidence playbooks across clients while keeping each client’s evidence in their own environment.
For healthcare-adjacent SaaS teams
Collect HIPAA security evidence without intentionally centralizing sensitive artifacts in another vendor’s cloud.
Security posture
Designed for sensitive evidence, not casual screenshots.
AuditFetch treats evidence as sensitive security data. The local runtime is designed around least privilege, local credential storage, audit logs, artifact hashing, and explicit user-controlled exports.
AI-assisted summaries are reviewable drafts, not compliance conclusions. AuditFetch does not use AI to certify compliance or make legal determinations.
Start local. Scale when you need to.
AuditFetch is designed for solo consultants, engineering-led SaaS teams, and enterprise private deployments.
Compliance Core
Billed monthly. USD per organization.
Annual option: $990/yr, billed annually upfront.
Getting SOC 2 evidence under control
- SOC 2 evidence collection, readiness tracking, review, and export
- Local read-only collectors for GitHub, AWS, Okta, Google Workspace, Jira, Linear, Datadog, and WorkOS
- Continuous collection — no evidence limits
- Local Team by default — unlimited members with no per-seat pricing
- 10 years of evidence history
- Gap analysis, reviewer workflow, and drift alerts
- Custom evidence automations
- PDF / ZIP / CSV auditor packets
- AI summaries, including local models
- Email support
Compliance Pro
Most popularBilled monthly. USD per organization.
Annual option: $1,490/yr, billed annually upfront.
Running SOC 2 and HIPAA together
- Everything in Core, plus HIPAA readiness
- Evidence can be reused across both frameworks after scope and review checks
- Local read-only collectors for GitHub, AWS, Okta, Google Workspace, Jira, Linear, Datadog, and WorkOS
- Continuous collection — no evidence limits
- Local Team by default — unlimited members with no per-seat pricing
- 10 years of evidence history
- Gap analysis, reviewer workflow, and drift alerts
- Custom evidence automations
- PDF / ZIP / CSV auditor packets
- AI summaries, including local models
- Email support
Compliance Advanced
Billed monthly. USD per organization.
Annual option: $2,990/yr, billed annually upfront.
Preparing for ISO 27001 certification
- Everything in Pro, plus ISO 27001 readiness
- Statement of Applicability lifecycle with approved snapshot pinning
- Risk references and separation-of-duties approval
- ISO audit packets
- Local read-only collectors for GitHub, AWS, Okta, Google Workspace, Jira, Linear, Datadog, and WorkOS
- Continuous collection — no evidence limits
- Local Team by default — unlimited members with no per-seat pricing
- 10 years of evidence history
- Gap analysis, reviewer workflow, and drift alerts
- Custom evidence automations
- PDF / ZIP / CSV auditor packets
- AI summaries, including local models
- Email support
ISO 27001 readiness and evidence workflows. AuditFetch does not issue certifications.
Frequently asked questions
Is AuditFetch a replacement for Vanta or Drata?
No. AuditFetch is designed to complement tools like Vanta and Drata. It focuses on collecting, validating, packaging, and syncing evidence.
Does AuditFetch certify SOC 2 or HIPAA compliance?
No. AuditFetch helps collect and organize evidence. It does not provide legal advice, guarantee auditor acceptance, or certify compliance.
Where is evidence stored?
With AuditFetch Local, evidence is stored in your environment unless you choose to export or sync it. Connected licensing and update services do not host your raw evidence. Managed cloud deployments have separate hosting arrangements; contact us to confirm availability and scope.
Why local-first?
Audit evidence often includes sensitive security configuration and access lists. Local-first deployment keeps evidence and credentials under your control.
Do we need to give AuditFetch write access?
No. AuditFetch should use read-only scopes by default. It is designed to collect evidence, not modify your infrastructure.
What are Custom Evidence Automations?
They adapt a reviewed read-only collector for AWS and GitHub. You preview and test the result before enabling it, and the capability is included in every Compliance plan.
Where do Custom Evidence Automation credentials live?
AuditFetch Local uses the integration credentials in your environment; do not put credentials or secrets in automation scope fields. Hosted deployments use their configured secret store.
Can Custom Evidence Automation connect any system?
No. It works with supported providers and reviewed operations. It is not a general-purpose no-code integration platform, and it does not accept arbitrary requests or embedded credentials.
Local-first, always
With AuditFetch Local, evidence and credentials stay in your environment by default. You control exports and synchronization to other systems.
Read-only, always
Never writes, remediates, or changes access to your systems.
Collect configuration evidence
Use supported configuration and access records. Do not upload patient data or secrets. Review source scope and redaction before collection.
Traceable evidence
See where evidence came from and when it was collected, with integrity checks and an audit log.
Ready to stop chasing audit screenshots?
See AuditFetch pricing and get started with local-first evidence automation for SOC 2, HIPAA, and ISO 27001.